Information security with business purpose.
Warden Risk Advisory helps organizations manage Information Security risks, strengthen governance, and protect the trust that supports their business.
Focused on security. Grounded in business.
Warden Risk Advisory is an independent advisory business focused on Information Security, risk management, and governance. We help organizations understand their risks, address business requirements, and develop practical security capabilities aligned with their operations.
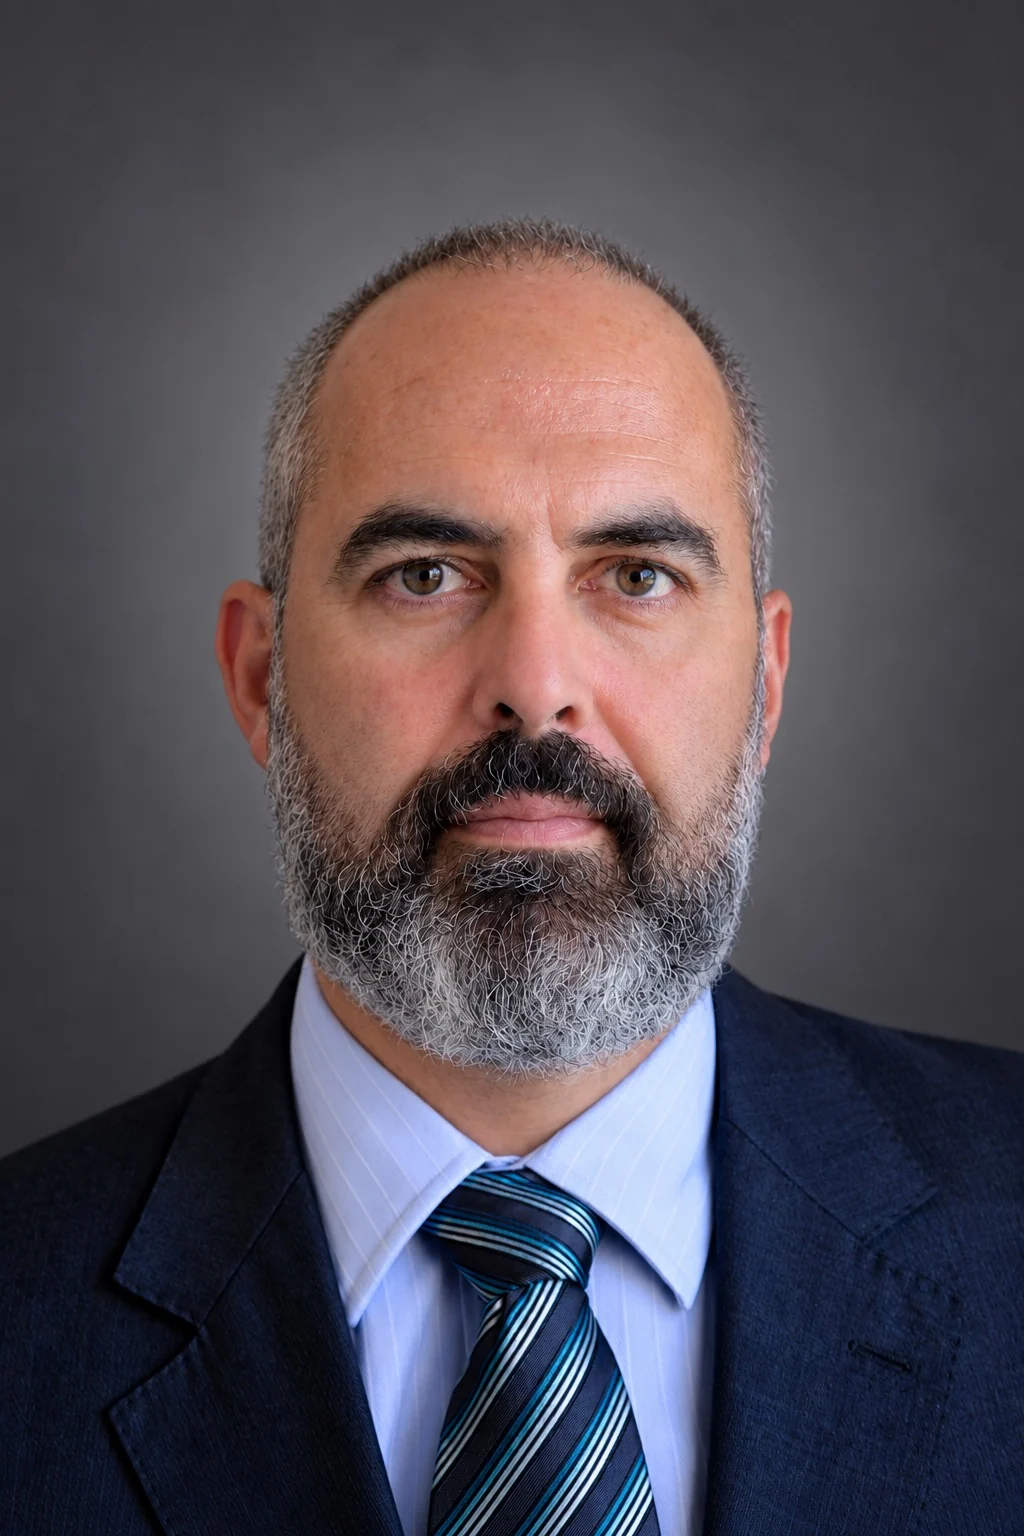
Marcelo Spinetti
Founder & Information Security Advisor
ISO/IEC 27001 Lead Implementer
Marcelo Spinetti is a mechanical engineer, holds a postgraduate qualification in Project Management, and is certified as an ISO/IEC 27001 Lead Implementer. His career combines business leadership, operations management, and information security, with professional experience in Brazil, the United Kingdom, and the United States.
He has held CISO responsibilities and worked on structuring and implementing information security management systems across several companies. His experience includes implementing a complete ISMS from the ground up and leading TISAX certification and recertification processes for automotive OEM suppliers.
At Warden Risk Advisory, this experience informs a practical approach: understanding the business, identifying risks, and structuring information security around each organization’s needs and priorities.
Understand first. Act with purpose.
We begin by understanding your business, risks, and existing capabilities. From there, we identify priorities and recommend practical actions that fit your operations, resources, and objectives.
Technical knowledge. Practical application.
We use recognized Information Security frameworks and standards to help organizations understand requirements, evaluate risks, and establish practical governance and security practices suited to their business.
Let’s talk about your security priorities.
Tell us about your business, current challenges, and objectives. We’ll help you identify how Warden can support your Information Security needs.